What it does
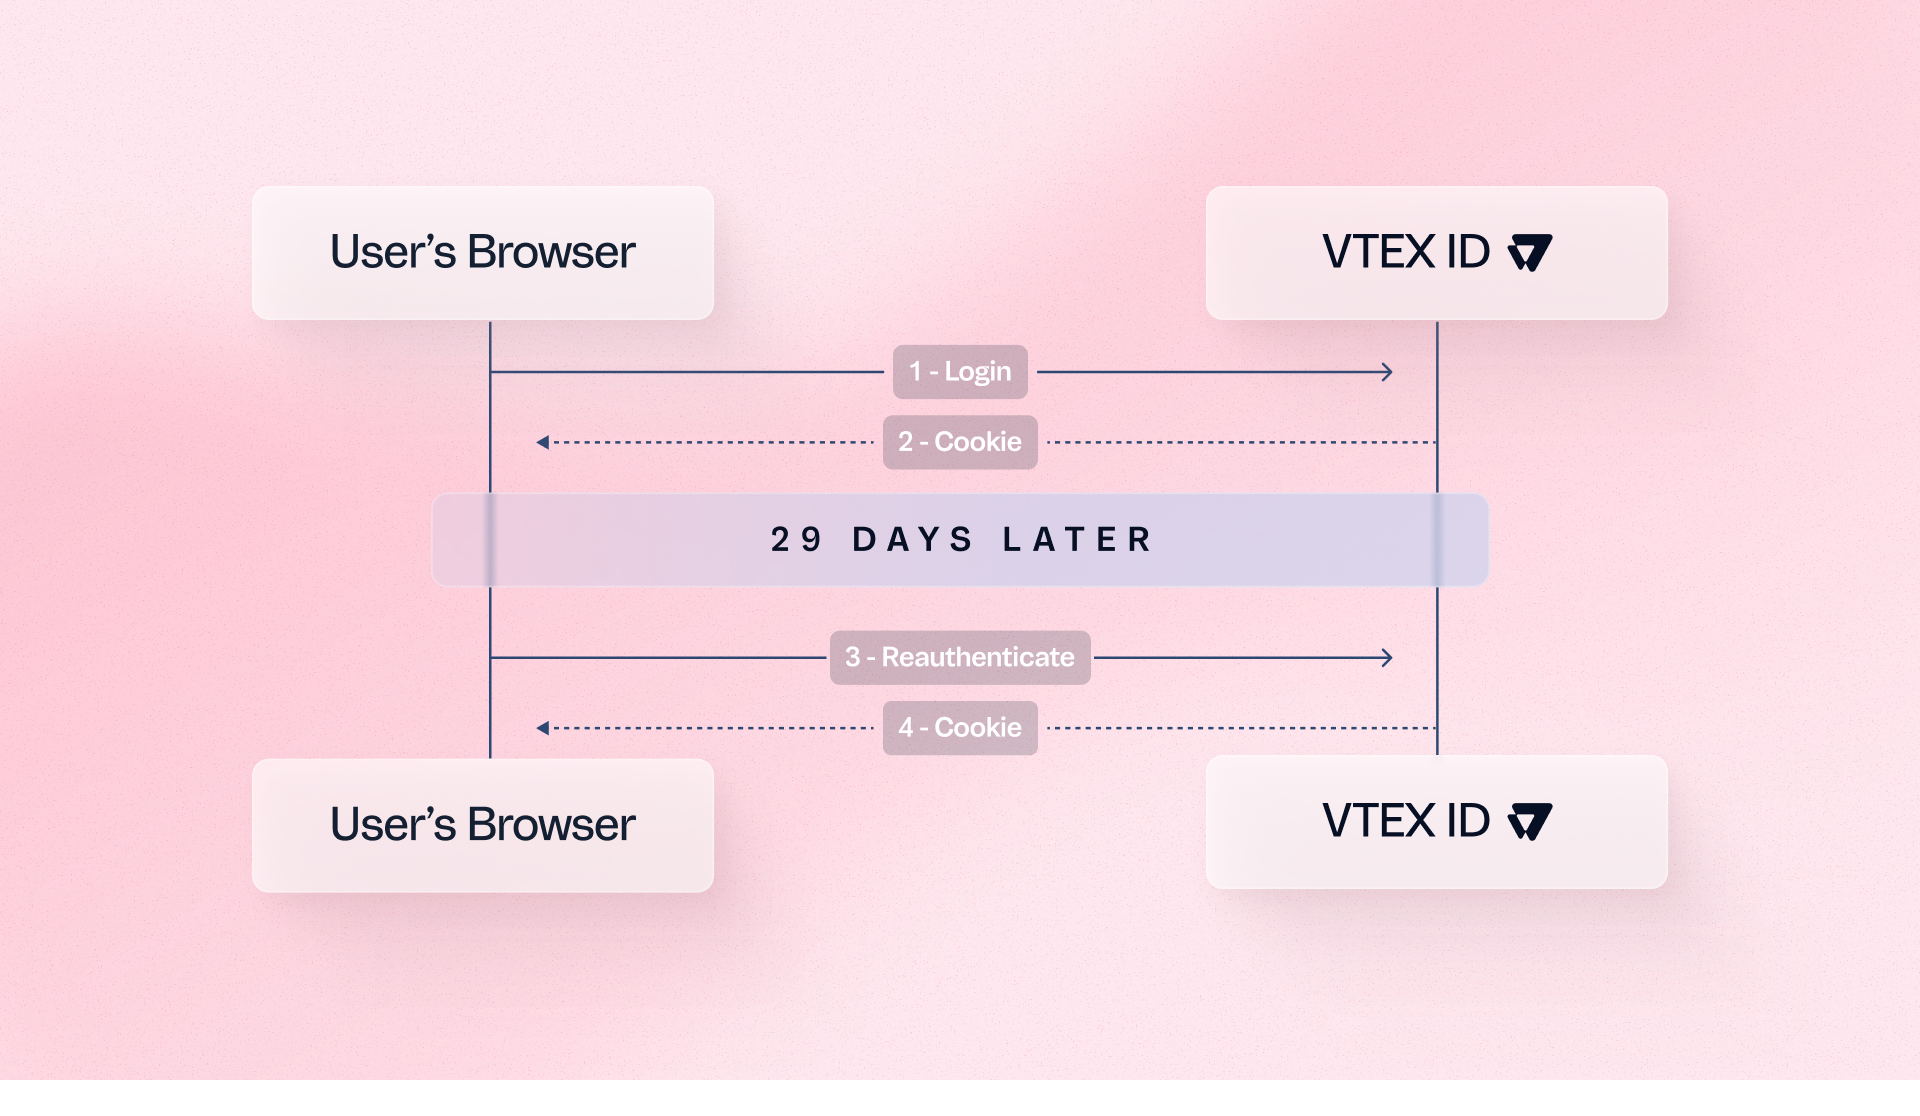
Enables secure session continuity for headless stores by introducing a refresh token flow that automatically renews expired access tokens for up to 30 days. When the access token expires, the system uses a valid refresh token to issue new credentials without requiring user interaction. This ensures consistent authentication behavior across all VTEX storefront architectures while maintaining secure token rotation.
Benefits
- Improved UX: Reduce login friction for returning shoppers logged in.
- Feature Parity: Ensure consistent session behavior across all VTEX storefront types
- Enhanced Security: Maintain high security standards with rotating tokens
- Higher conversion: Minimize session drop-offs during the purchase journey
How to use
Contact VTEX Support to request the activation and configuration (1, 7, or 30 days). For FastStore, enable the feature through the FastStore SDK. For headless implementations, update your authentication middleware to call the renewal endpoint using the refresh token.